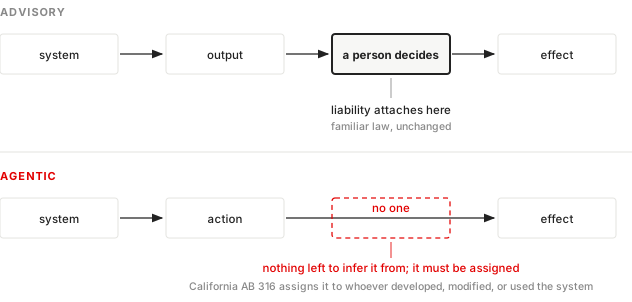
Advisory. The system produces an output and a person decides. A fraud score a reviewer acts on, a draft a lawyer edits, a risk flag a clinician confirms. A person sits in the causal chain, so responsibility follows familiar paths.
Agentic. The system takes the action itself. Coding agents such as Claude Code can run code, browse, edit files, and send requests, and no person necessarily stands between each decision and its effect.
Why this is where liability changes
In an advisory system, the person who decided is the obvious place for responsibility to land. In an agentic system that link is missing. California AB 316, in force since January 1, 2026, closes one door: a defendant cannot argue that the AI acted autonomously. The remaining liability analysis depends on the applicable law and facts. More in Who is liable when AI acts?
Most deployments sit in between
Few systems are purely one or the other. The middle ground is built from four controls:
- Approval thresholds. The system acts alone below a limit and asks a person above it.
- Review after the fact. The system acts, and a person checks the record later.
- Escalation rules. Defined cases go to a person, whatever the threshold says.
- Hard limits. Some actions the system may not attempt at all.
They differ in when they work. Thresholds, escalation, and hard limits act before the effect. Review after the fact acts on the record, so at the moment of the action the system was agentic, whatever the review later finds. That is a reasonable design for low-stakes actions and a poor one for anything that cannot be reversed.
What to check
- List what each system does without approval. For every AI system in use, write down the actions it can take before a person signs off. That list is its agentic side, whatever the product calls itself.
- Make the hard limits enforced. A limit in a policy document is advice to the system. A limit checked before the action runs is a control. See Are your AI controls enforced, or just written down?
- Record which agent acted, on whose authority. Review after the fact is only as good as the record it reviews. See Can you prove afterwards who did what?
Sentinel, an AI gateway, is a hard limit of one kind. It blocks a request the policy does not allow, such as one asking the model to insult a customer, and records metadata for each request. It checks the prompt on its way out and leaves the model's response unchanged.
Frequently asked questions
- What is the difference between a system that advises and one that acts?
- With advisory AI the system produces an output and a person decides before anything happens, such as a fraud score a reviewer acts on or a draft a lawyer edits. With agentic AI the system takes the action itself, and no person necessarily stands between its decision and the effect.
- Why does liability change when an AI acts on its own?
- In an advisory system the person who decided is the obvious place for responsibility to land. In an agentic system that link is missing, so responsibility has to be assigned. California AB 316, in force since January 1, 2026, closes one door: a defendant cannot argue that the AI acted autonomously. The remaining analysis depends on the applicable law and facts.
- What controls sit between advisory and agentic?
- Four: approval thresholds, where the system acts alone below a limit and asks a person above it; review after the fact; escalation rules that send defined cases to a person; and hard limits on actions the system may not attempt. Thresholds, escalation, and hard limits act before the effect, while review after the fact acts on the record.
- Is review after the fact enough for an AI agent?
- It is a reasonable design for low-stakes actions and a poor one for anything that cannot be reversed. Review acts on the record, so at the moment of the action the system was agentic, whatever the review later finds. Review is also only as good as the record it reviews.
- How do you find out how agentic your AI systems are?
- For every AI system in use, list the actions it can take before a person signs off. That list is its agentic side, whatever the product calls itself. Then make sure the hard limits are checked before the action runs, and that the record shows which agent acted and on whose authority.
Keep going
What is the OWASP Top 10 for LLM applications?
What is prompt injection, and how do you defend against it?
Map one workflow before the next one goes wrong
A practical next step
For regulated work
Sources
- California Assembly Bill 316 (Krell), Artificial intelligence: defenses, chaptered October 13, 2025, effective January 1, 2026. Bars specified defendants from asserting that AI acted autonomously to cause harm.
- European Union, Artificial Intelligence Act, Articles 14 and 15, human oversight and accuracy, robustness, and cybersecurity of high-risk systems.